
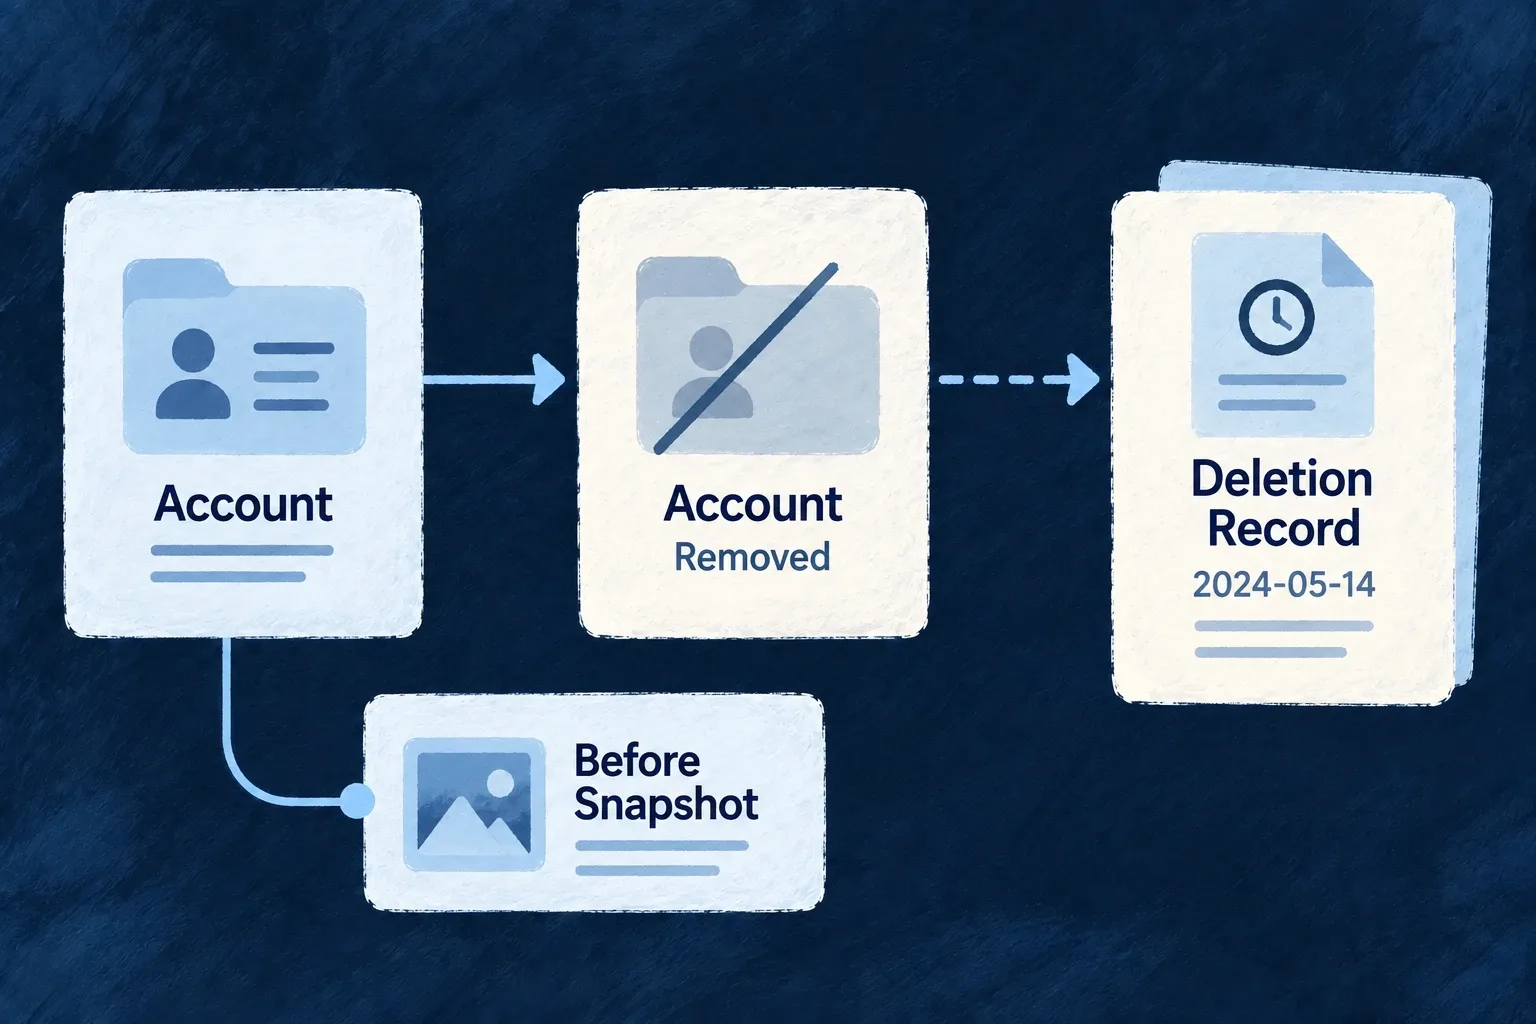
Keep the evidence after an account is removed
Account deletion should not erase the explanation of what happened. Wildo records completed user and organization deletion using the pre-deletion subject details, and keeps audit records outside the organization’s deletion cascade.
Example — Keep evidence after an account is removed
A scheduled purge removes an organization after its recovery window. The deletion event still identifies the organization and actor even though its business record is gone.
For engineers
A deletion handler receives utils.currentObject, the subject fetched before persistence. The deletion and configured cascade complete before the postfix emits the event. The snapshot supplies identity and descriptive fields that cannot be reread after removal.
The organization hook preserves the original operation result:
Selected source from organization-deletion-audit.custom-impl.backend.service.ts:
operationPath: {
  resourceIdentifier: CoreResourceType.ORGANIZATIONS,
  operationIdentifier: CoreResourceOperation.DELETE,
  variantType,
  isOperationDefault: variantKey === undefined,
  variantKey,
},
debugLabel: `organizations.delete${variantKey ? `.${variantKey}` : ''}.audit`,
handlers: {
  postfixCoreOperations: async (_id, result, executionContext, _operationPath, utils) => {
    await emitOrganizationDeletedAudit(container, _id, executionContext, utils);
    return result;
  },
},
This selected registration is inside createOrganizationDeletionAuditFactory. The factory is registered for both the internal scheduled-purge variant and the administrator API variant, so the same physical deletion fact is observed through either declared path.
Keep lifecycle facts distinct
A request for deletion marks the lifecycle transition and starts its configured window. A deletion event records the later physical removal. Restoring during the window is therefore not contradictory evidence: request, restore and completed destruction are different facts.
The organization-to-audit relationship excludes audit rows from parent deletion. Access to surviving evidence follows the audit viewing contract; it does not recreate the removed customer account. Apply the application’s evidence-retention and privacy decisions to those surviving records.
Post-commit recording errors are reported separately rather than telling the caller a completed deletion was rolled back. When adding a destructive application operation, preserve the pre-state needed for evidence and register its observation on every declared execution variant.