
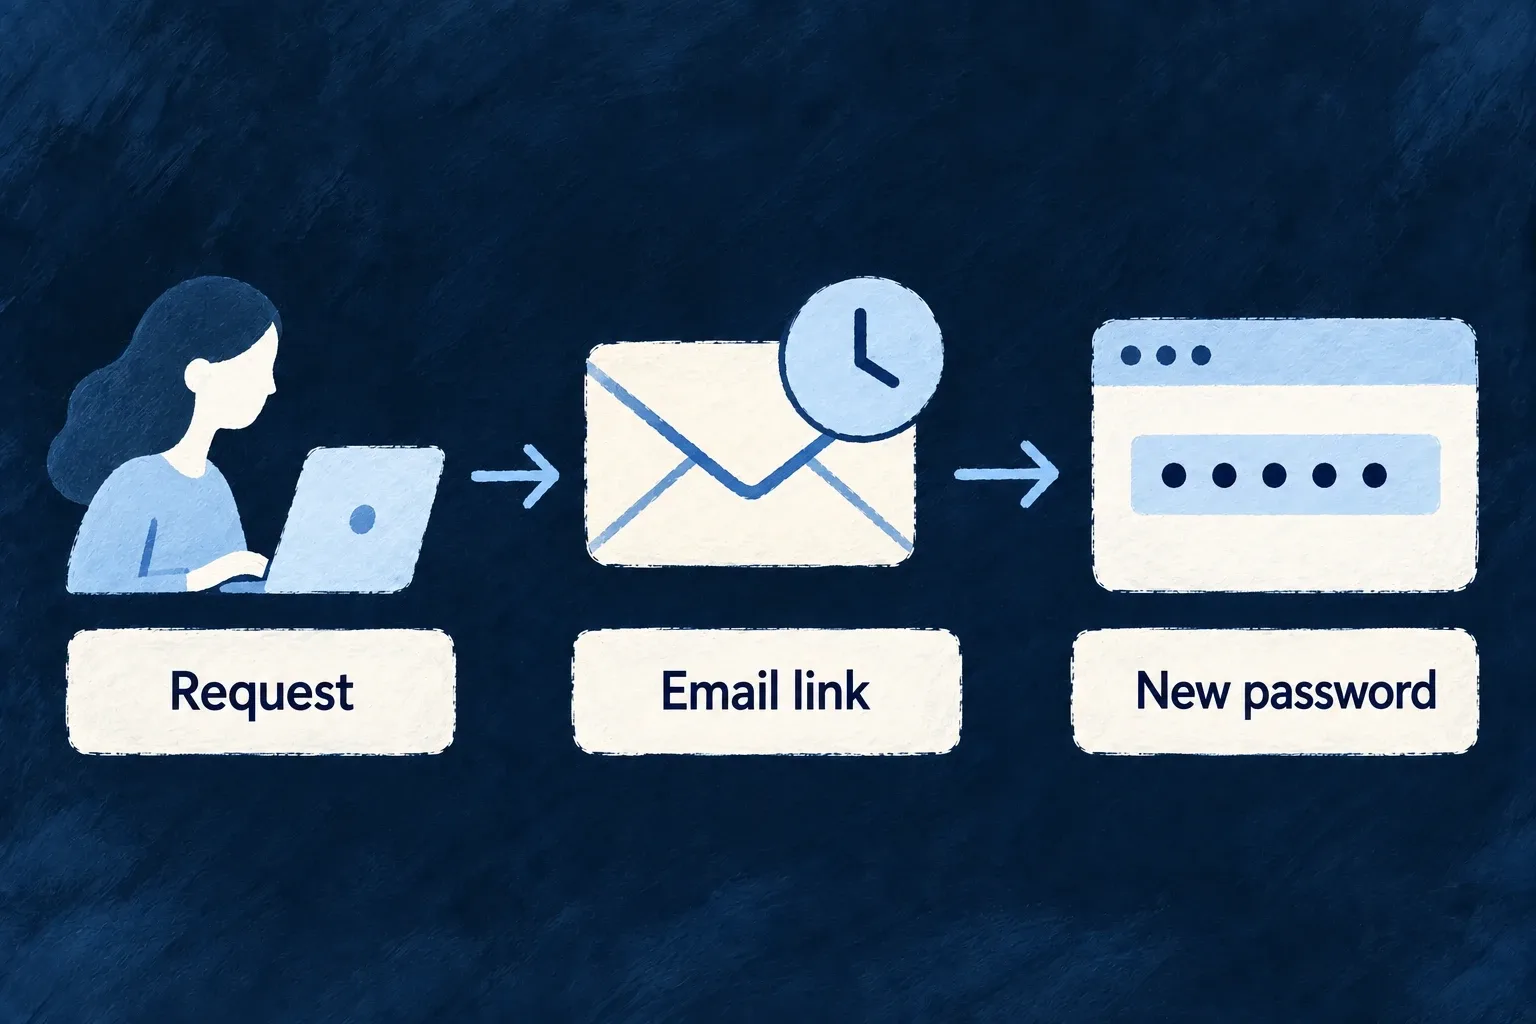
Recover access through your inbox
Let people replace a forgotten password using an expiring email link. Wildo checks the replacement against the account’s policy and withdraws earlier tokens when the change completes.
The request response does not reveal whether an address belongs to an active account.
Example — Replace a forgotten password
A person requests recovery, opens the email and sets a new password. Their older sessions must authenticate again.
For engineers
Keep request and completion separate
The request handler returns the same response for unknown, eligible and ineligible accounts. ACTIVE and PENDING_VERIFICATION accounts can receive a single-use password-reset token by transactional email; suspended, inactive and deleted accounts do not receive it. Auth_PasswordLost supplies the standard request and completion interface.
Apply the current account policy
The completion service consumes the token, verifies its purpose and resolves the account’s effective password policy. After validation, the actual credential-changing sequence is:
const newPasswordHash = await this.credentialVerifier.hashPassword(newPassword, this.appConfigService.config.auth.passwordHashing);
await this.tokenIssuer.invalidateAllTokensForUser(userId);
await this.credentialVerifier.updatePasswordHash(ec, userId, newPasswordHash);
await this.consumableTokenService.revokeTokensByRelatedId(userId, CoreConsumableTokenTypes.PASSWORD_RESET);
The hash is derived using configured password hashing. Earlier account tokens are withdrawn before the credential is written, and sibling password-reset links are revoked. A custom recovery screen should submit to this completion operation rather than update a user record directly.
Make the retry behavior understandable
The token is consumed before password-policy validation. A rejected replacement can therefore require another recovery email; the same link is not a reusable validation session. Present the known password requirements before submission and preserve the resend path.
A pending-verification account can receive recovery mail without becoming active. Restoring a suspended or deactivated account remains a separate lifecycle action. The completion endpoint limits requests to 10 per minute per IP before parsing or hashing; the request endpoint has its own throttles.