
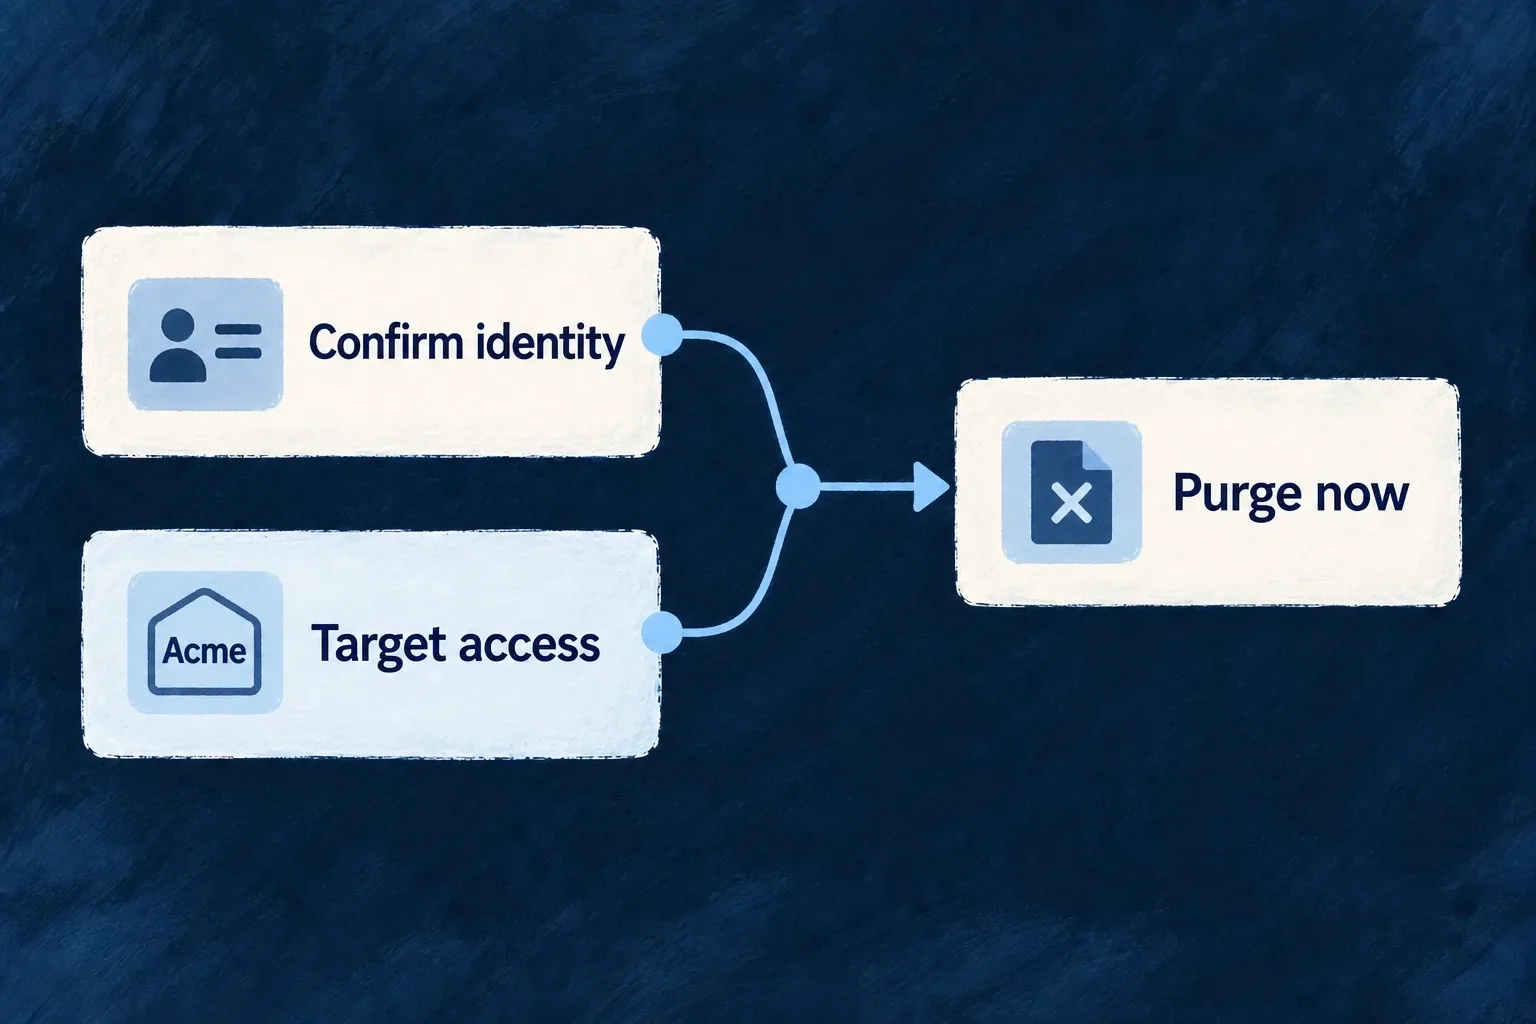
Require a fresh check before permanent removal
Immediate deletion is a separate, destructive action. It bypasses the recovery period and requires the administrator to prove their identity again before removing the organisation.
Platform role alone is not unlimited reach: this action remains within its declared tenant boundary. The normal deletion-request path provides the reversible option.
Example — Confirm the irreversible action
An authorised administrator chooses permanent deletion. A previously signed-in session is not enough; the operation requires fresh re-authentication before the deletion can proceed.
For engineers
Read the operation requirement independently of risk labels
The administrator delete variant declares requiresStepUpAuthentication: true. This is the operative requirement; a risk label alone is not equivalent.
The following excerpt shows the security-relevant contract, with surrounding operation configuration omitted:
{
  roles: [CORE_APP_ROLES.APP_ADMIN_SUPER_ADMIN],
  riskLevel: ResourceOperationRiskLevel.HIGH,
  requiresStepUpAuthentication: true,
}
Use the generated administrator delete operation and its re-authentication flow. The service handler checks the per-operation requirement rather than accepting an old login merely because it is still a valid session.
Address the administrator variant explicitly
The HTTP operation is DELETE /organizations/{organizationId}/admin. The default DELETE variant is internal and route-less; it is what the scheduled purge uses. There is no ordinary tenant-facing delete route to use instead.
For a platform super-administrator who also has legitimate scope access to the target workspace:
curl -X DELETE "$BACKEND_URL/organizations/$ORG_ID/admin" \
  -H "Authorization: Bearer $ADMIN_TOKEN" \
  -H "x-reauth-token: $REAUTH_TOKEN"
Obtain REAUTH_TOKEN from the application’s step-up flow for that same authenticated caller. The fresh proof accompanies the request as x-reauth-token; a still-valid login token by itself does not satisfy the operation. This route performs the purge immediately rather than setting a future deadline.
Keep tenant reach as a separate check
This irreversible door does not declare cross-tenant platform administration. A non-member operator cannot infer permission from the role or from a recovery grant used by a different operation. A successful fresh identity check proves the caller again; it does not manufacture tenant access.
Preserve a meaningful deletion record
The deletion audit implementation captures the organisation’s identity before removal and emits after the delete. Both the administrator variant and the scheduled internal deletion variant register the hook.
Verify the refused cross-tenant request, the missing-step-up request and the allowed deletion separately. Only the last should remove the row. For ordinary customer offboarding, request deletion keeps the recovery interval available.