
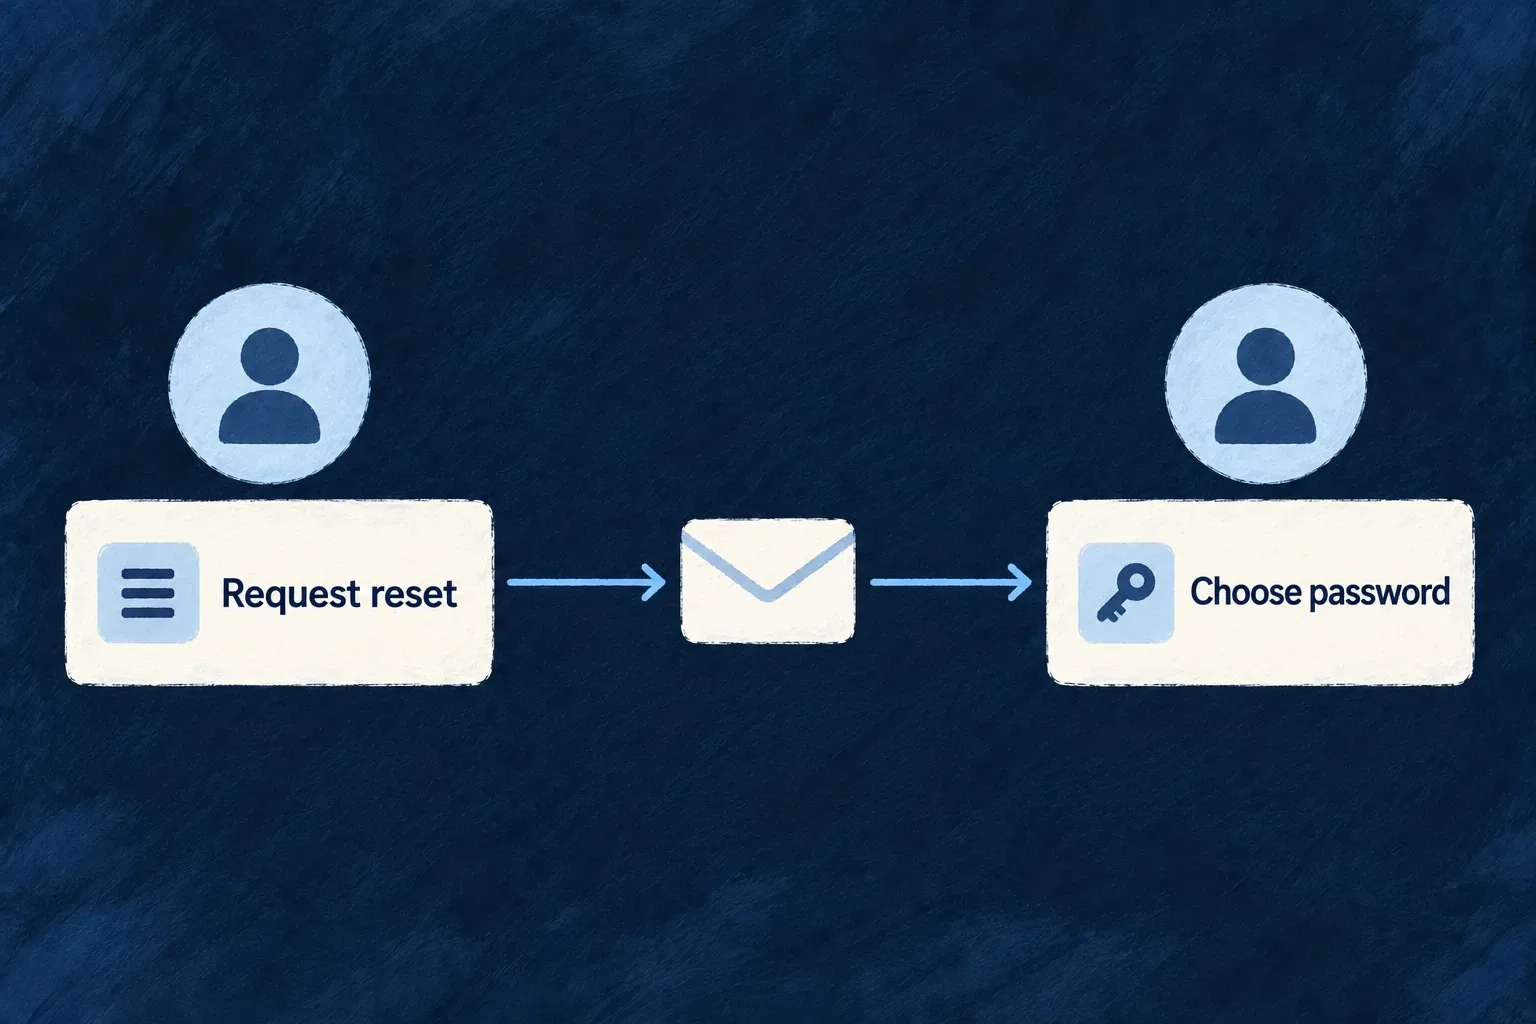
Require a password reset without seeing the new password
An administrator can initiate a password reset for another account, withdraw its existing sessions and send the replacement link to the account owner.
The action records who requested it and why. The administrator receives confirmation, not a link that lets them choose someone else’s password.
Example — Respond to a suspected credential leak
An administrator provides a reason for resetting a member’s password. Existing sessions are withdrawn and the member receives the reset email.
For engineers
Use the dedicated administrative operation
The FORCE_PASSWORD_RESET variant is application-super-admin gated and explicitly admits a different target user. Its request and response contracts are selected here from users.shared.resources-config.schemas.ts:
requestDto: z.object({
  reason: z.string().min(1).max(500)
}),
customResponseDto: z.object({
  expiresAt: z.date(),
  sessionsRevoked: z.boolean()
}),
The custom implementation requires one addressed account, an attributable caller and a non-empty reason. Self-reset is refused here; the account owner’s normal password-change path proves their current credential instead.
Observe what the operation actually returns
expiresAt describes the emailed link and sessionsRevoked confirms withdrawal. Neither the reset token nor URL is returned to the administrator. The shared password-reset service sends to the target user’s email using the transactional template and resolved locale.
Separate containment from completion
Existing tokens are invalidated before the forced-reset flow completes. The user then follows the mail and chooses a password that meets their effective policy. Starting the reset is not evidence that the owner has received the email or changed the password yet. Delivery configuration and operational monitoring therefore remain necessary alongside the account action.
The backend refuses a deleted target. Reset initiation does not reactivate a suspended account or assign new roles; those are separate lifecycle decisions.